SURFsecureID supports the use of FIDO tokens (also called authenticators or security keys). Both FIDO U2F and FIDO2 tokens can be used as a 2nd factor.
The FIDO protocols are standardized, so that tokens from different manufacturers can be used. See below for the options.
Supported FIDO tokens
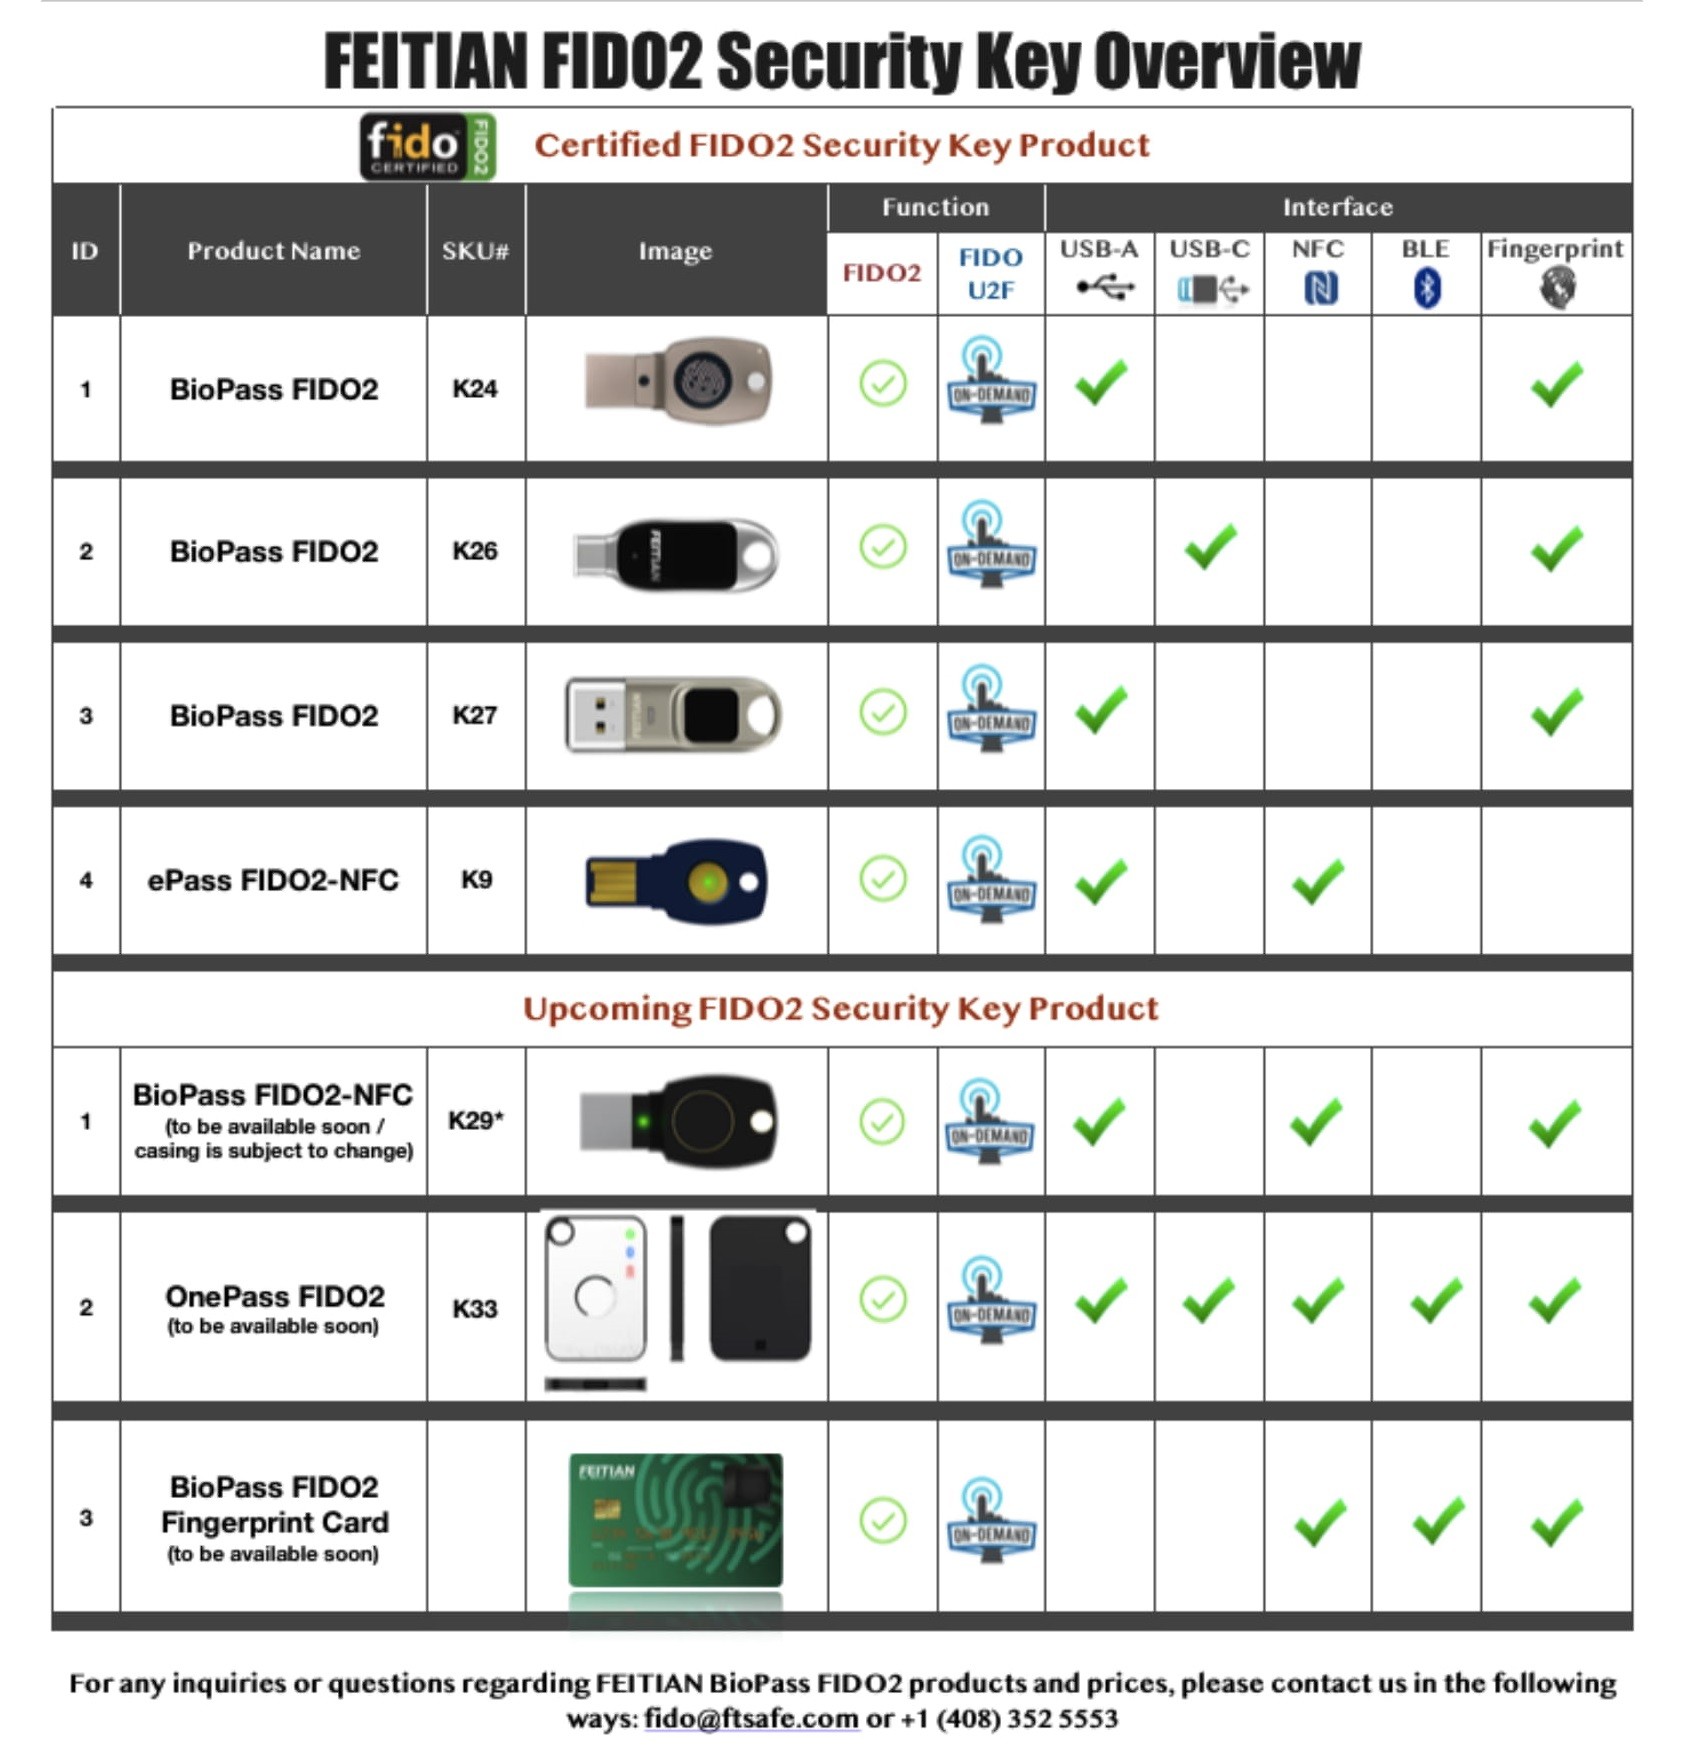
Feitian
The following types of Feitian tokens are suitable for FIDO with SURFsecureID.
- MultiPass FIDO (K25)
- ePass FIDO2 (A48) and ePass FIDO2 NFC (K9)
- BioPass FIDO2 (K26 and K27)
- AllinPass FIDO2 (K27) and AllinPass FIDO2 Plus
See the Feitian website for an overview of the different FIDO tokens.
The following types of Google tokens are suitable for FIDO with SURFsecureID:
- Titan Security Key (all versions).
The Titan Key from Google is currently not available in the Netherlands.
Solokeys (pending)
The following types of Solokeys are currently under investigation to be added to SURFsecureID:
- Solo
- Solo Tap
- Somu
NB: the Solo Hacker will not be supported.
Yubico
The following types of YubiKey tokens are suitable for FIDO with SURFsecureID.
- YubiKey 5 (FIDO2). Available in different shapes (USB-A with NFC, USB-C, nano, 5Ci)
- Yubikey FIPS (FIDO U2F). Available in different shapes (nano, USB-A, USB-C).
- YubiKey 4 (FIDO U2F). Available in different shapes (nano, USB-A, USB-C). No longer in production.
- YubiKey Neo (FIDO U2F, RFID and NFC compliant). No longer in production.
- YubiKey Edge (FIDO U2F compliant). No longer in production.
- Yubico Security Key Series (the "blue keys").
- Except the variant called "FIDO U2F Security Key". No longer in production.
See the Yubico website for an overview of the different YubiKeys. If you don't know which Yubikey you have, you can check this here on the Yubico website.
| 5 | 4 | Neo | Security Keys |
|---|---|---|---|
|
|  |
|


Another token?
FIDO is a technology that allows secure login to websites with an authenticator. Such an authenticator can be a USB token, but also a mobile phone or something that is built into a laptop and which can be used via facial recognition or a fingerprint scanner, for example). Some authenticators are suitable for use in 2-factor authentication. These tokens are therefore supported in SURFsecureID.
The following requirements are set for authenticators for use in SURFsecureID:
- It really has to be a second factor, i.e. something other than a "what-you-know" factor such as a password. Because FIDO uses public key cryptography, this means that the authenticator must have special hardware to protect the generated private keys. This special hardware (cryptographic chips) makes it extremely difficult to read the private keys. If such a private key can be read, a copy can be made of the authenticator, and the authenticator thus lapses from a "what-you-have" factor to a "what-you-know" factor. There is therefore no longer any question of 2-factor authentication.
- When registering FIDO authenticators as the 2nd factor, SURFsecureID checks which type of authenticator is used. This is done on the basis of an attestation certificate that is programmed into the authenticator by the manufacturer. Based on that attestation certificate, SURFsecureID determines which type of authenticator is involved and whether it is suitable for protecting private keys with cryptographic hardware.
- New FIDO authenticators are constantly appearing on the market. SURF assesses those products and manages an allow list of approved FIDO authenticators in SURFsecureID. It is possible that new products have not yet been evaluated by SURF. In such a case, you can contact support@surfconext.nl.
In summary, FIDO authenticators are supported by SURFsecureID if the following conditions are met:
- The FIDO authenticator complies with the FIDO standard (FIDO / U2F or FIDO2 / CTAP).
- The FIDO authenticator has an attestation certificate from the manufacturer with which the type of authenticator can be determined.
- The FIDO authenticator uses cryptographic hardware to protect private keys.
Overview
Content Tools